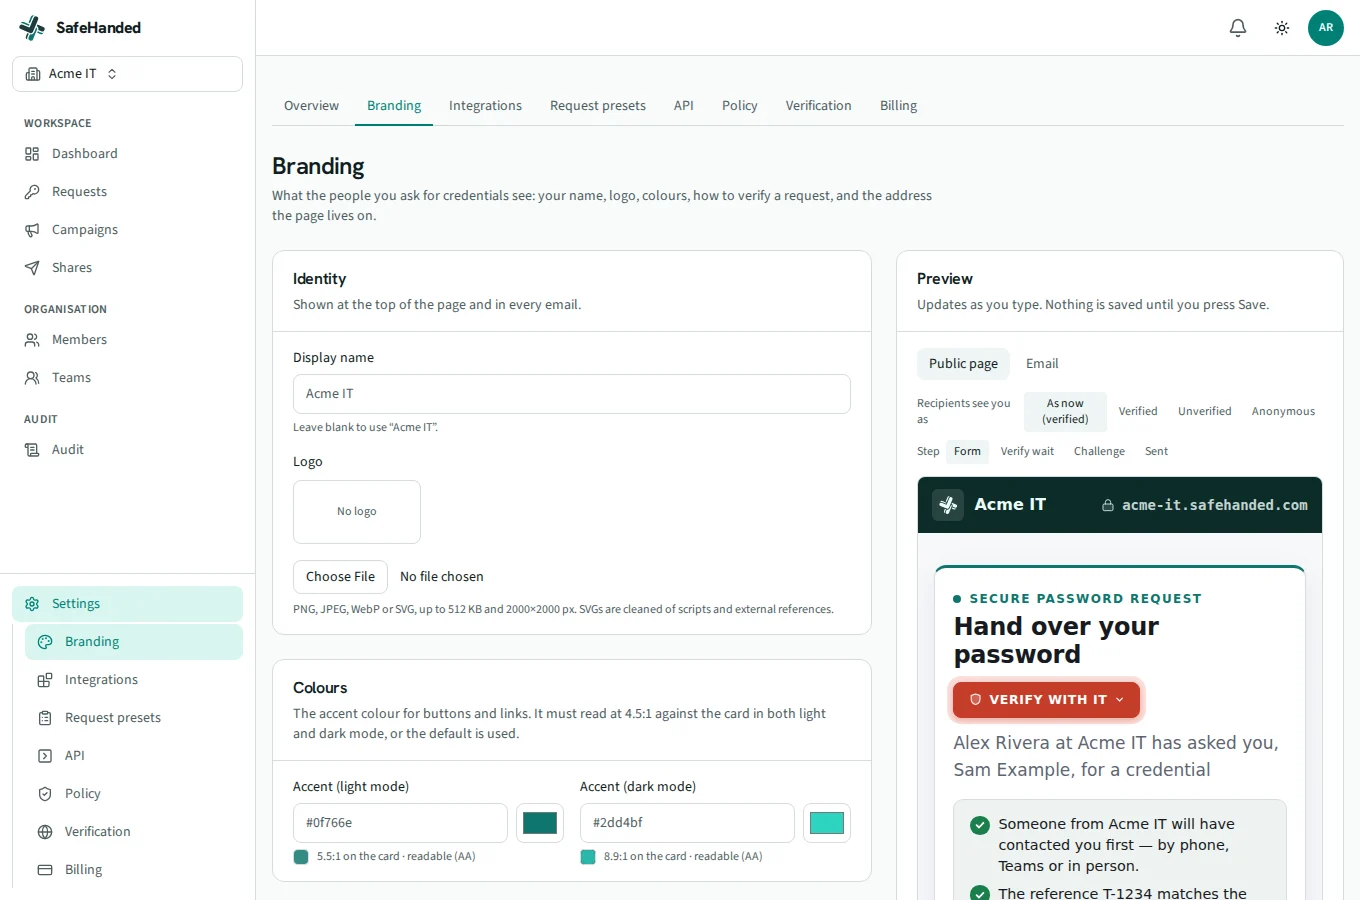
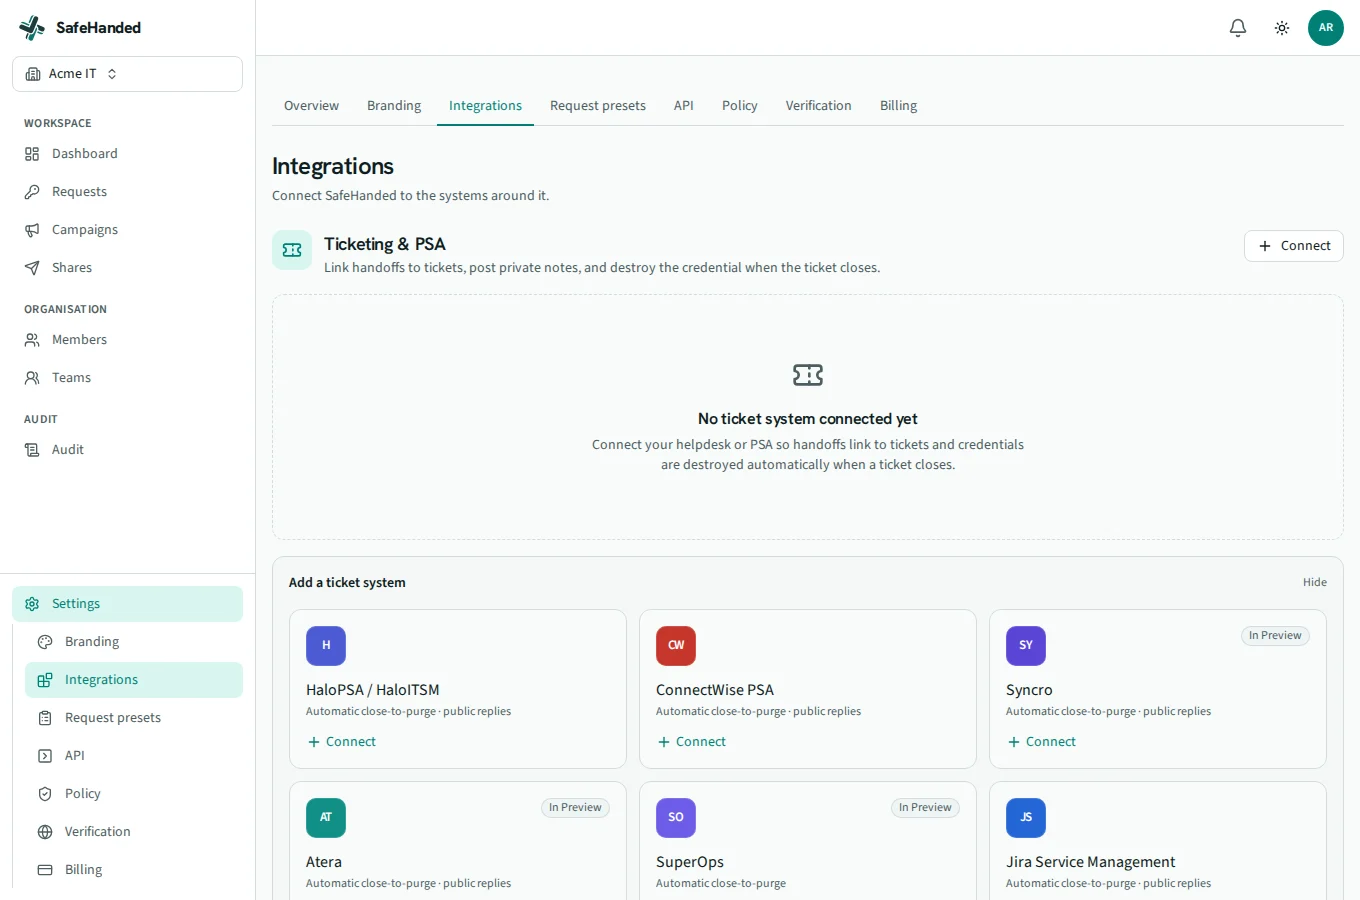
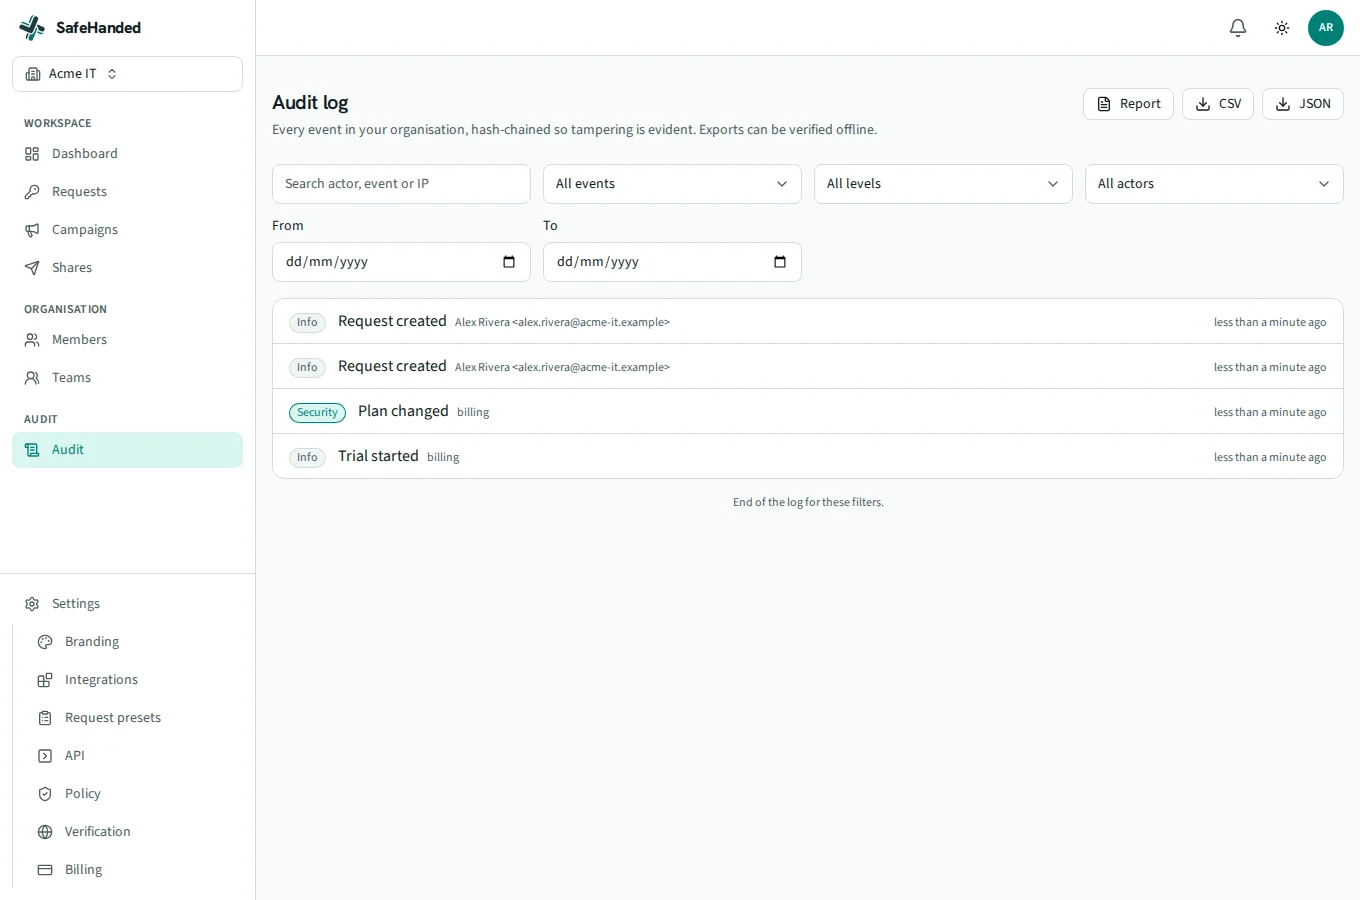
Per-client branding and domains, a PSA-linked workflow, and audit evidence your clients and their cyber-insurers can actually read. On a tool whose vendor can't read the secret.


Cyber-insurance renewals and client audits ask the same question: how do you handle user credentials? Instead of a paragraph of assurances, hand them evidence.

Most link tools can decrypt every secret they hold, so a breach at the vendor, or a rogue operator, is a breach of every client you serve. SafeHanded only ever stores ciphertext, sealed to one technician's passkey. There is no readable secret on our side to leak, subpoena or misconfigure.
Branding, domains, directories and audit trails are scoped to the client, enforced below the UI.
Portable keys, an optional org recovery key and tested offboarding, so a technician leaving never strands a client's credential.
Bulk campaigns, a public API (OpenAPI 3.1) and signed webhooks to fit SafeHanded into your existing automation.
One flat plan for your whole client base, with technicians so cheap that seats never block adoption. Auditors, including your clients' auditors, are always free.
£1,490/year · 10 technicians included, then £8 each
Start a 14-day MSP trial with no card, bring in a client or two, wire up your PSA, and see the evidence for yourself before you commit.